





Information management and cybersecurity

Information management and cybersecurity
CYBERSECURITY
GOVERNANCE OF CYBERSECURITY
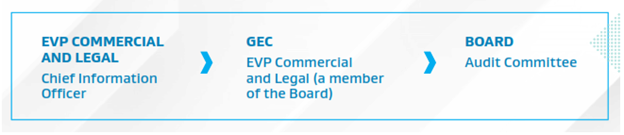
At Sasol, we place a high priority on maintaining strong cybersecurity practices and protecting our digital assets. We have built our governance structure to maintain security standards in every aspect of our business operations. Our board members, who have a multitude of experience in technology, risk management, and strategic decision-making, are responsible for overseeing our cybersecurity approach. Executive management oversees cybersecurity policies and making sure they are in line with the broader goals of the business.
INFRASTRUCTURE VULNERABILITY
Our infrastructure undergoes comprehensive third-party vulnerability assessments, to strengthen the overall security of our systems and data by assisting us in proactively identifying and fixing possible weaknesses. Our infrastructure has various certification to ensure that that we adherence to industry best practices and standards. In addition, where we use third party solutions, we perform due diligence assessment and or require SOC2 type 2 compliance.
Management
The CIO has an experienced team of IT professionals that ensure that IT and Digital requirements of the Sasol Business are met in a secure and effective manner.
CIO
The CIO reports to the Audit Committee on a quarterly basis and the committee oversees the embedment of the cybersecurity strategy, progress on key cyber projects, reviews report on potential security threats and incidents and assesses the effectiveness of cyber security controls.
Cyber Security teams
The Chief Cyber Security Officer (CCSO) drives the implementation of the cybersecurity strategy to protect the organisation’s digital assets and to ensure the confidentiality, integrity and availability of data and systems.
Protection of our operational environment
We have a 24x7 Security Operation Centre (SOC) to provide further protection from cyber-attacks to ensure safety and availability. A team of internal and external cyber security experts are at the CIO and CCSO disposal to detect, protect, respond, and recover from Cyber threats.
Training and awareness
We have a company wide information security awareness and training program that our employees are enrolled. This is managed by a s security training platform and focus is placed on critical topics to improve cybersecurity awareness. We also run regular awareness campaigns and communication to highlight and emphasize cybersecurity risk to employees. We create visibility of training compliance using what we call cyber personal risk scores (C-PRS). This provides a dashboard of cybersecurity training compliance to individual employees, line managers to get a view of their respective team’s compliance status as well as to executive leaders on the state of cyber awareness training compliance across their portfolio’s. By using this mechanism of visibility and accountability we ensure cybersecurity training compliance remains high.
Additional information can be found in our 2024 Integrated Report and the Form 20-F for the year ended 30 June 2024.